Connections
Password, SSH key with passphrase, ssh-agent · Interactive server prompts, including the server’s own second factor · ProxyJump through a bastion · Agent forwarding to a host · Keep-alive for long sessions
ssh client for linux · terminal · sftp · port forwarding · mcp
A full SSH client: terminal, file browser, port forwarding. Works offline and without an account — and Claude Code, Codex or Cursor can work out what is happening on your machines without ever seeing a password or a private key.
01 — the agent · mcp
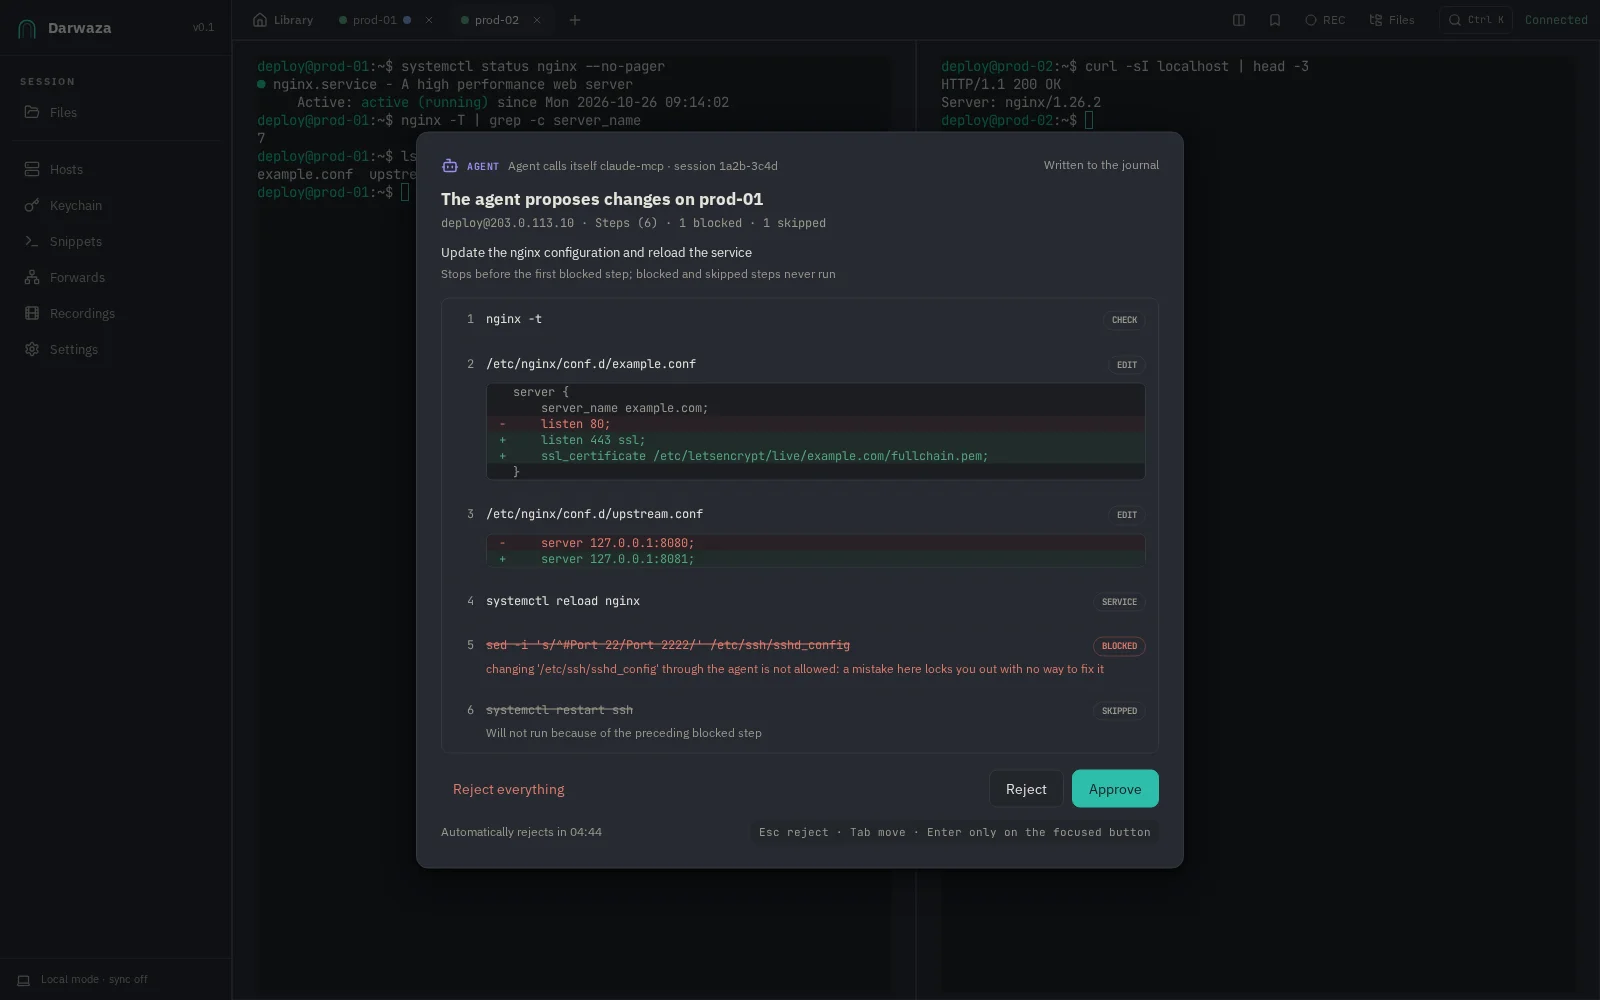
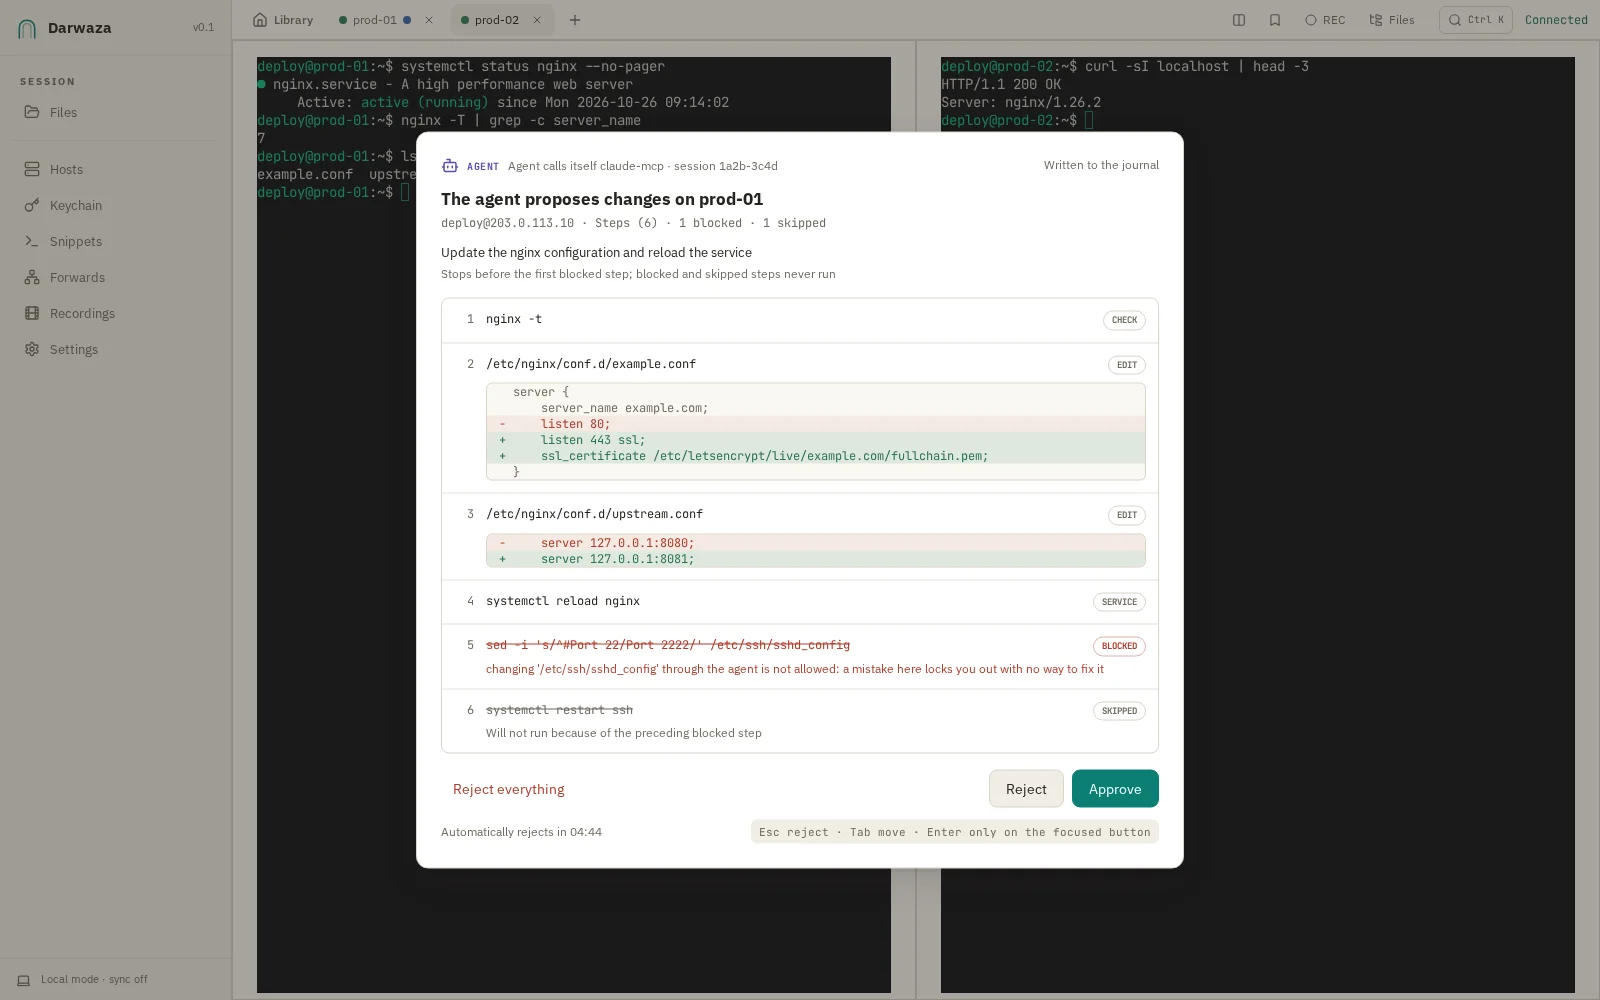
Point Claude Code, Codex or Cursor at the app and the agent can work out what is going on across your machines. The credentials stay here: the agent names a host, Darwaza does the connecting. Nothing appears on the server itself — no agent, no service, no dependencies: to it this is an ordinary SSH session, the same as yours. So it also works where nothing can be installed.
Reconnaissance the hosts open to it, a read-only command, a server summary in one call — system, disk, memory, listening ports, failed services — file search, a log of what has already been done on this server, and notes about the server it keeps itself.
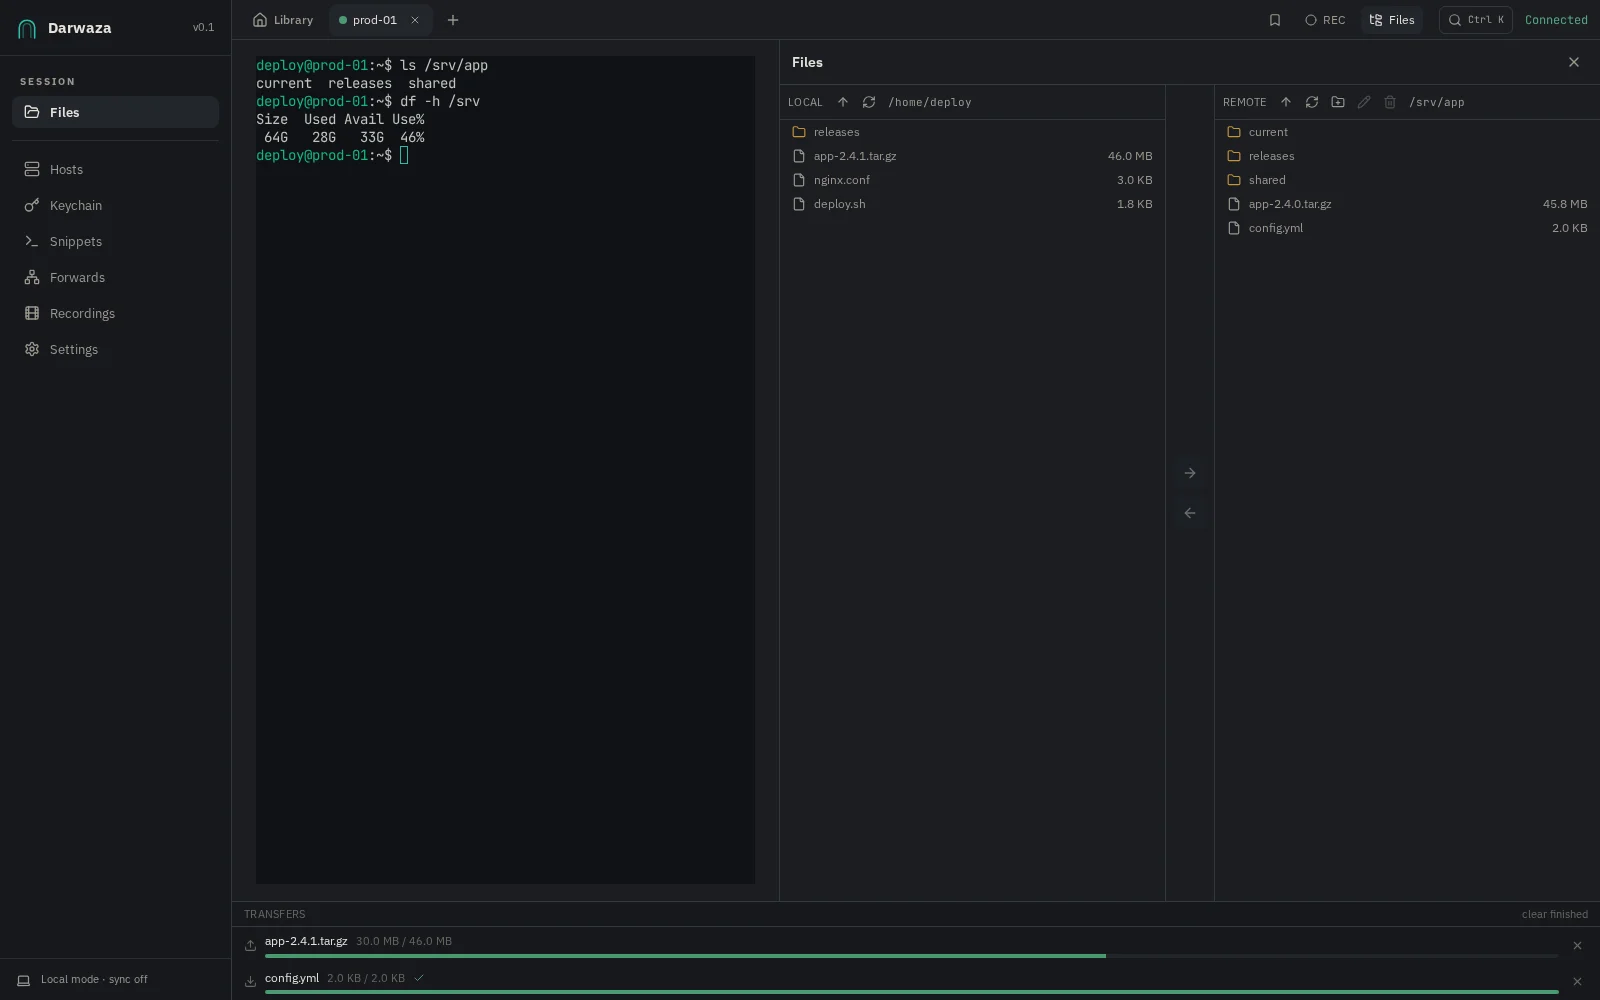
Files read, list a directory and stat a file, download and upload, make a directory, rename, delete, patch instead of resending the whole file, and copying server to server directly, bypassing your disk.
Actions a plan of changes — you see every command before the first one runs; restarting a service with a config check before and a state check after; your snippets, if you opened them; a temporary port forward to an internal service; a tab with the command typed in — you press Enter.
02 — what it does
Password, SSH key with passphrase, ssh-agent · Interactive server prompts, including the server’s own second factor · ProxyJump through a bastion · Agent forwarding to a host · Keep-alive for long sessions
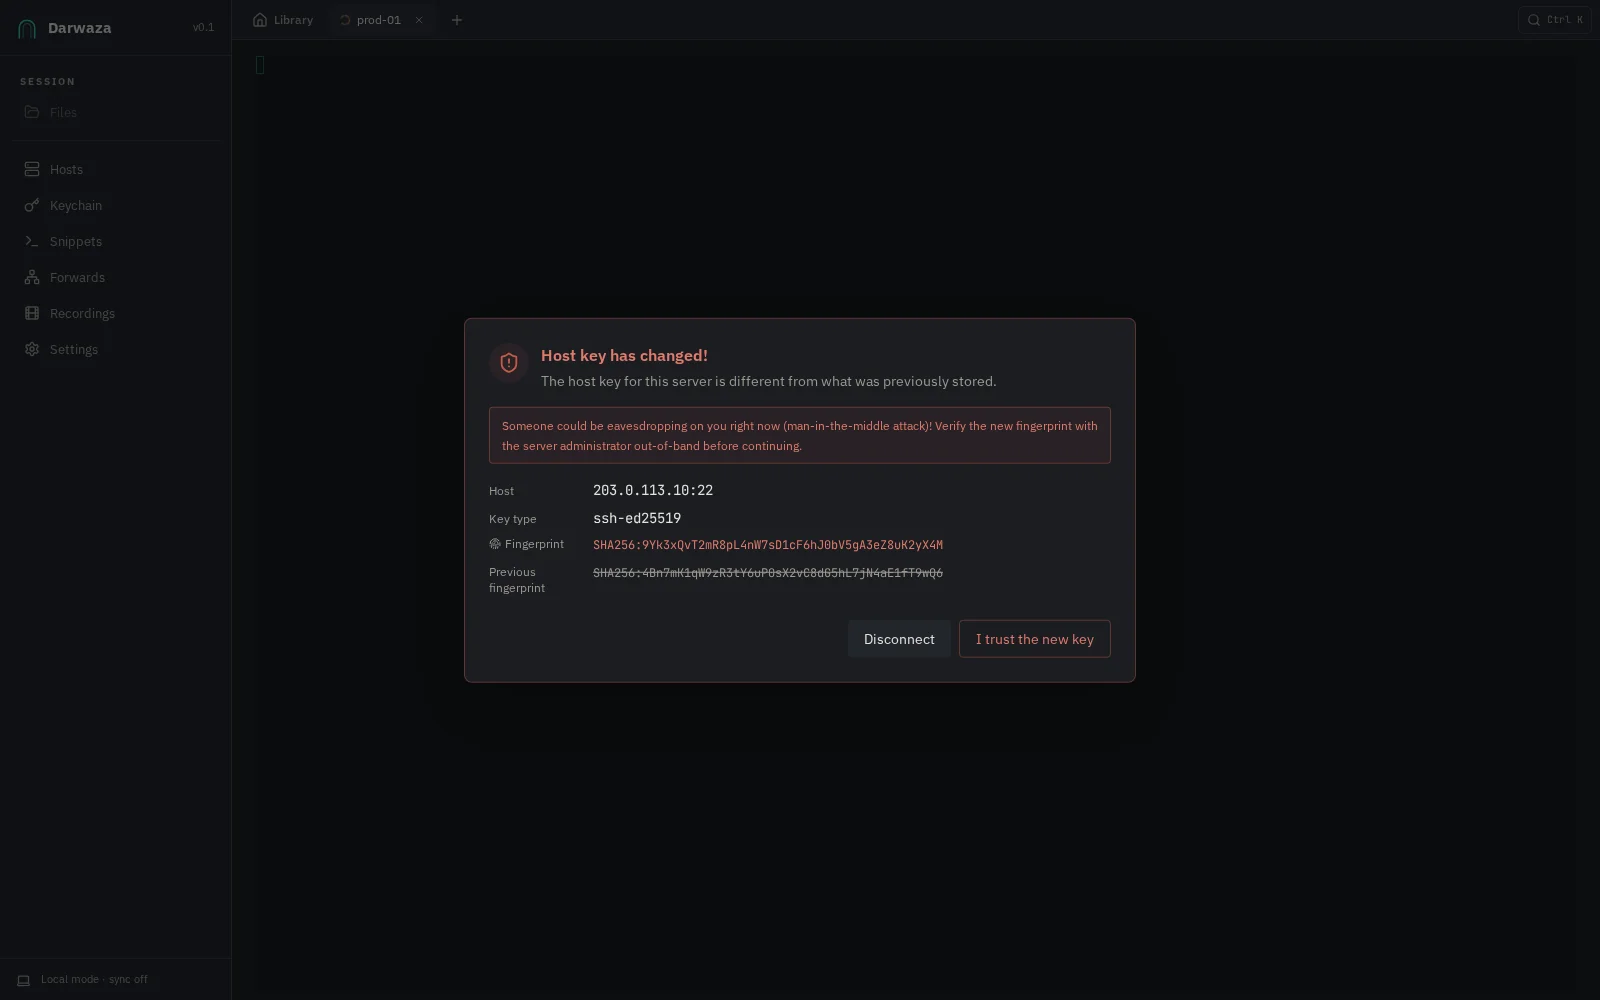
TOFU: the fingerprint is stored on first connection · A separate warning when a server key changes · Import from ~/.ssh/config and ~/.ssh/known_hosts
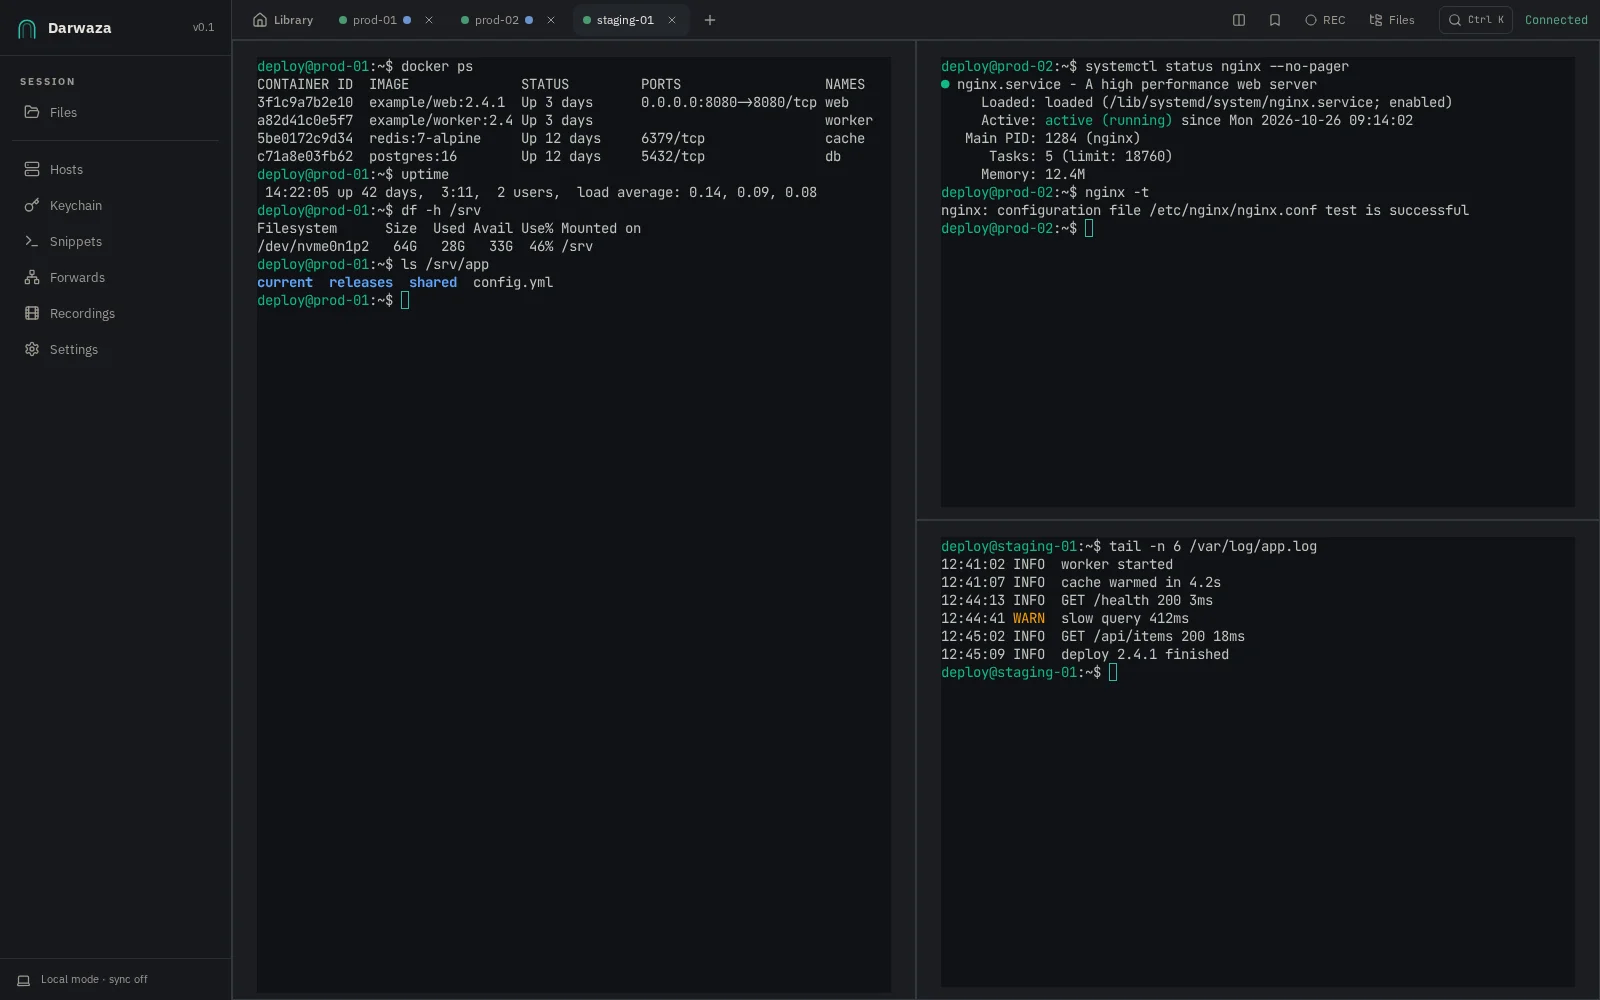
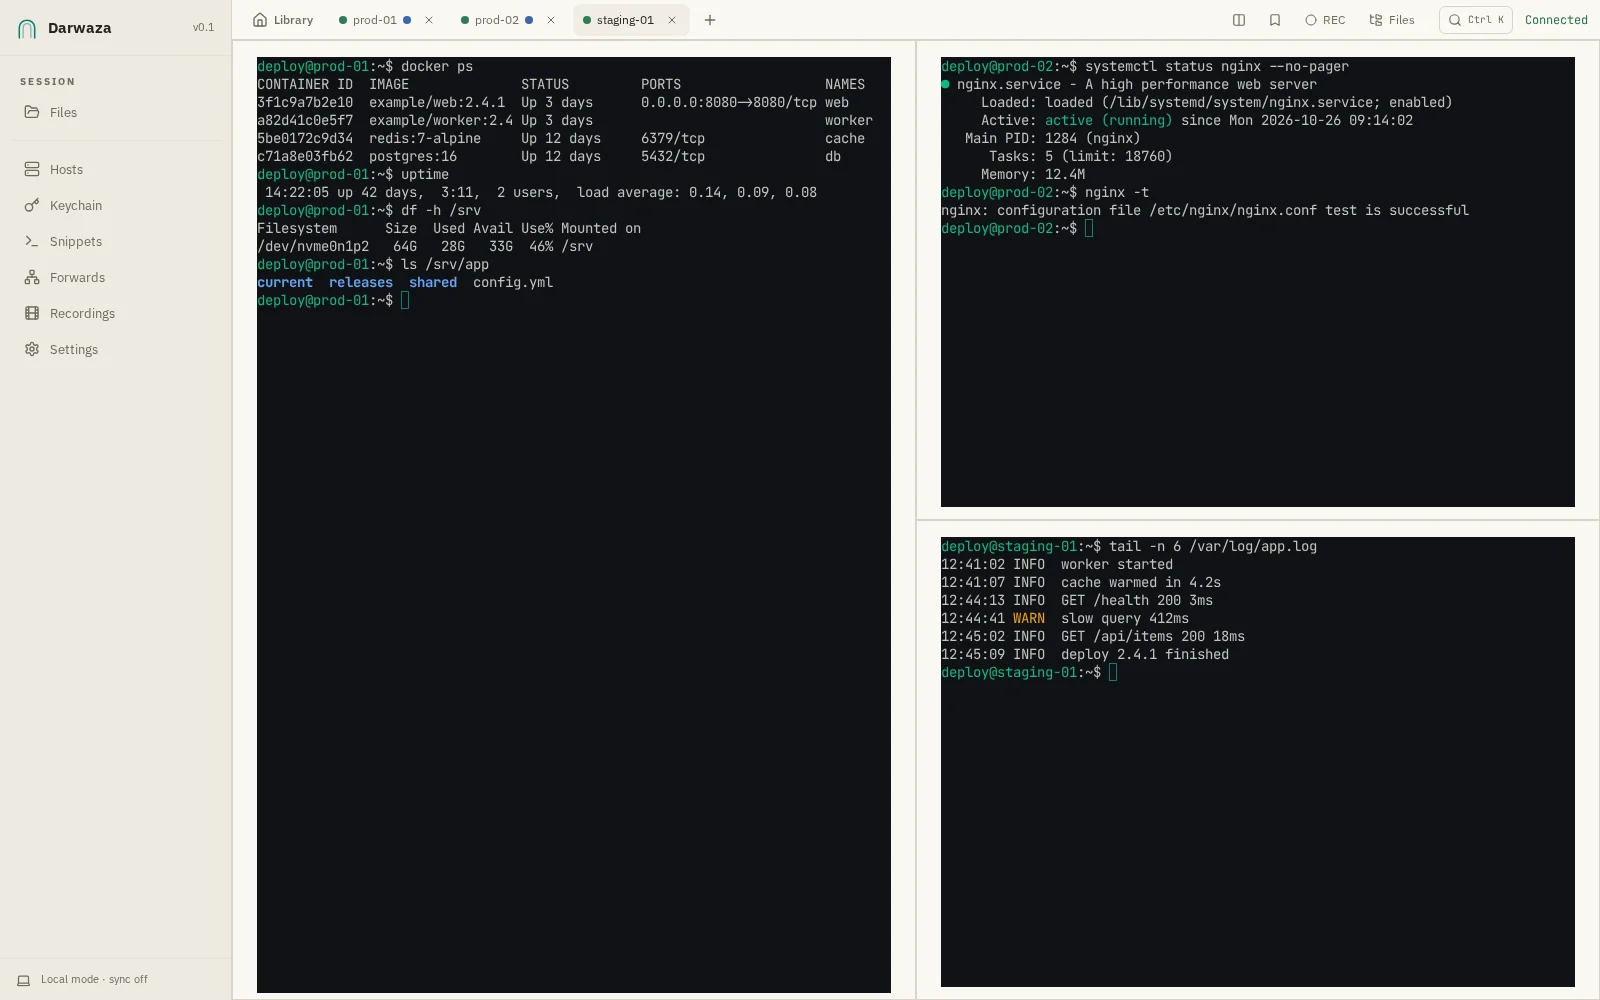
Tabs and up to four side-by-side panes · Drag tabs between panes · Search the output and bookmark places in it · Themes and font settings
Two-pane SFTP browser · Drag between panes and from your system file manager · Transfer panel with progress and cancel · Create folders, rename, delete
Local (-L) · Remote (-R) · Dynamic SOCKS5 (-D)
Command snippets · Session recording in asciinema format · Connection history · Six interface languages · A master password on top of the system store, with a recovery key · Two-factor on unlocking
03 — what makes it different
Fully, not in a trimmed-down mode. This is a principle, not a free tier: signing up is not a condition of launching the app and never will be.
The encryption key is derived from your password on your device and never leaves it. We state the consequence ourselves: the password cannot be recovered, and there will never be a "reset by email". Access to the data comes back only with the recovery key.
None at all. Crash reports are files on your disk, collection is off by default, and they are sent only to the address you typed in. No counters, no trackers — this page included.
We connect to servers as plain ssh does: the server picks the authentication method, not us. We do not "improve" SSH beyond recognition.
asciinema, not a format of our own: they play with the stock asciinema play, convert with third-party tools and stay valid even if the session drops. No lock-in.
Uzbek, Russian, English, Kazakh, Kyrgyz and Turkish — complete, not half-done. Three of them are hard to find anywhere else.
Today we build for Linux only, and that is what the page says. A site promising five platforms and delivering one loses trust exactly once.
04 — data location
+your email address · when and from which IP you signed in · a list of devices with the names you gave them · how many records you have, their types and modification times · the size of each encrypted blob · your encrypted second-factor secret
−host names and addresses · logins · passwords · private keys and passphrases · the contents of anything at all
05 — security
No "military-grade encryption" — specifics you can check.
$darwaza --security
·Argon2id: 64 MiB of memory, 3 passes
·AES-256-GCM for records, a fresh random nonce every time
·The key is derived on your device and never leaves it
·Secrets in the system keyring or in a store behind a master password
·TOFU with an explicit warning when a server key changes
Your data is encrypted with a key we do not have: we cannot guess your password or send you a new one. That is why a recovery key is issued when you sign up — 32 characters to copy onto paper and put away; if you do not have one, you can issue a new key in the cabinet while you are signed in. Lose both the password and the key, and nobody can bring the server copy back. What stays on the device is your local data; if it is under a master password, that has its own recovery key.